
Apigee Edge 문서입니다.
Go to the
Apigee X 문서로 이동합니다. info
다음 섹션에서는 Apigee Edge 및 Private Cloud용 Edge의 알려진 문제를 설명합니다. 대부분의 경우 나열된 문제는 향후 출시 버전에서 해결될 예정입니다.
Miscellaneous Edge known issues
The following sections describe miscellaneous known issues with Edge.
| Area/Summary | Known issues |
|---|---|
Cache expire results in incorrect cachehit value |
When the Workaround: Repeat the process (make second call) again right after the first call. |
Setting InvalidateCache Policy
PurgeChildEntries to true does not work correctly |
Setting Workaround: Use the KeyValueMapOperations policy to iterate cache versioning and bypass the need for cache invalidation. |
| Concurrent deployment requests for a SharedFlow or API proxy can result in an inconsistent state in the Management Server where multiple revisions are shown as deployed. |
This can happen, for example, when concurrent runs of a CI/CD deployment pipeline occur using different revisions. To avoid this problem, avoid deploying API proxies or SharedFlows before the current deployment is complete. Workaround: Avoid concurrent API proxy or SharedFlow deployments. |
| API call counts shown in Edge API Analytics might contain duplicate data. |
Edge API Analytics can sometimes contain duplicate data for API calls. In that case the counts shown for API calls in Edge API Analytics are higher than the comparable values shown in third-party analytics tools. Workaround: Export the analytics data and use the gateway_flow_id field to de-duplicate the data. |
Edge UI의 알려진 문제
다음 섹션에서는 Edge UI의 알려진 문제를 설명합니다.
| 영역 | 알려진 문제 |
|---|---|
| 조직이 ID 영역에 매핑되면 탐색 메뉴에서 Edge SSO 영역 관리 페이지에 액세스할 수 없습니다. | 조직을 ID 영역에 연결하면 더 이상 왼쪽 탐색 메뉴에서 Admin > SSO를 선택하여 Edge SSO 영역 관리 페이지에 액세스할 수 없습니다. 이 문제를 해결하려면 다음 URL을 사용하여 페이지로 바로 이동합니다.(https://apigee.com/sso). |
통합 포털의 알려진 문제
다음 섹션에서는 통합 포털에 대해 알려진 문제를 설명합니다.
| 영역 | 알려진 문제 |
|---|---|
| SmartDocs |
|
| SAML ID 공급업체 | SAML ID 공급업체를 사용한 단일 로그아웃 (SLO)은 커스텀 도메인에 대해 지원되지 않습니다. SAML ID 공급업체를 사용하여 커스텀 도메인을 사용 설정하려면 SAML 설정을 구성할 때 로그아웃 URL 필드를 비워둡니다. |
| 포털 관리자 |
|
| 포털 기능 |
|
Known issues with Edge for Private Cloud
The following sections describe the known issues with Edge for Private Cloud.
| Area | Known issues |
|---|---|
| Edge for Private Cloud 4.53.01 |
NGINX Vulnerability Assessment (CVE-2026-42945)
A vulnerability (CVE-2026-42945) was disclosed affecting the Impact on Apigee Edge for Private Cloud: Apigee Edge for Private Cloud is not affected by this vulnerability in its default, shipped configuration. The exploitability of CVE-2026-42945 is dependent on specific NGINX configuration patterns, notably the use of the Action Required:
|
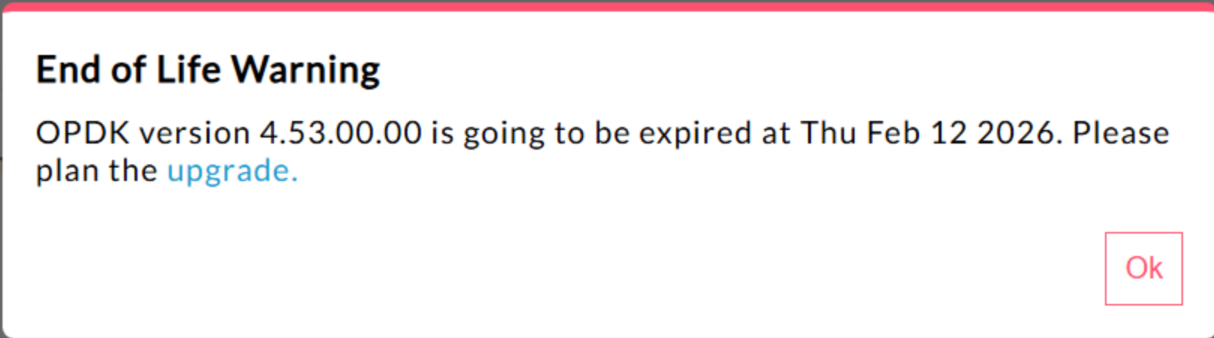
| Edge for Private Cloud 4.53.00 | 440148595: End of Life Popup Warning Displayed Excessively
In Edge for Private Cloud 4.53.00 and later, the UI displays an
"End of Life" (EOL) warning pop-up. This warning
appears There is currently no method available for users to disable or reduce the frequency of this EOL warning. |
| Edge for Private Cloud 4.53.01 |
Java Callouts
Customer Java callouts that attempt to load the Bouncy Castle cryptography provider using the name "BC" might fail because the default provider has been changed to Bouncy Castle FIPS to support FIPS. The new provider name to use is "BCFIPS". |
| Edge for Private Cloud 4.53.00 |
Java Callouts
Customer Java callouts that attempt to load the Bouncy Castle cryptography provider using the name "BC" might fail because the default provider has been changed to Bouncy Castle FIPS to support FIPS. The new provider name to use is "BCFIPS". |
| Edge for Private Cloud 4.52.01 Mint update |
This issue affects only those who are using MINT or have MINT enabled in Edge for Private Cloud installations. Component affected: edge-message-processor Issue: If you have monetization enabled and are installing 4.52.01 as a fresh install or upgrading from previous Private Cloud versions, you will encounter an issue with message processors. There will be a gradual increase in open thread count leading to resource exhaustion. The following exception is seen in edge-message-processor system.log: Error injecting constructor, java.lang.OutOfMemoryError: unable to create new native thread |
| Apigee HTTP/2 vulnerability | A Denial-of-Service (DoS) vulnerability was recently discovered in multiple implementations of the HTTP/2 protocol (CVE-2023-44487), including in Apigee Edge for Private Cloud. The vulnerability could lead to a DoS of Apigee API management functionality. For more details, see Apigee Security Bulletin GCP-2023-032. The Edge for Private Cloud router and management server components are exposed to the internet and can potentially be vulnerable. Although HTTP/2 is enabled on the management port of other Edge-specific components of Edge for Private Cloud, none of those components are exposed to the internet. On non-Edge components, like Cassandra, Zookeeper and others, HTTP/2 is not enabled. We recommend that you take the following steps to address the Edge for Private Cloud vulnerability:
Follow these steps if you are using Edge Private Cloud versions 4.51.00.11 or newer:
Follow these steps if you are using Edge for Private Cloud versions older than 4.51.00.11:
|
| Postgresql upgrade when updating to version 4.52 | Apigee-postgresql is having issues with upgrading from Edge for Private Cloud version 4.50 or 4.51 to version 4.52. The issues mainly occur when the number of tables is greater than 500. You can check the total number of tables in Postgres by running the SQL query below: select count(*) from information_schema.tables Workaround: When Updating Apigee Edge 4.50.00 or 4.51.00 to 4.52.00, be sure to perform the preliminary step before upgrading Apigee-postgresql. |
| LDAP policy | 149245401: LDAP connection pool settings for JNDI configured through the LDAP resource are not reflected, and JNDI defaults cause single-use connections each time. As a result, connections are being opened and closed each time for single use, creating a large number of connections per hour to the LDAP server. Workaround: In order to change the LDAP connection pool properties, do the following steps to set a global change across all LDAP policies.
To verify that your connection pool JNDI properties are taking effect, you can perform a tcpdump to observe the behavior of the LDAP connection pool over time. |
| High Request Processing Latency | 139051927: High proxy processing latencies found in the Message Processor are affecting all API Proxies. Symptoms include 200-300ms delays in processing times over normal API response times and can occur randomly even with low TPS. This can occur when than more than 50 target servers in which a message processor makes connections. Root cause: Message processors keep a cache that maps target server URL to HTTPClient object for outgoing connections to target servers. By default this setting is set to 50 which may be too low for most deployments. When a deployment has multiple org/env combinations in a setup, and have a large number of target servers that exceed 50 altogether, the target server URLs keep getting evicted from cache, causing latencies. Validation: To determine if target server URL eviction is causing the latency problem, search the Message Processor system.logs for keyword "onEvict" or "Eviction". Their presence in the logs indicate that target server URLs are getting evicted from the HTTPClient cache because the cache size is too small. Workaround:
For Edge for Private Cloud versions 19.01 and 19.06, you can edit and configure the HTTPClient
cache, conf/http.properties+HTTPClient.dynamic.cache.elements.size=500 Then restart the message processor. Make the same changes for all message processors. The value 500 is an example. The optimal value for your setup should be greater than the number of target servers that the message processor would connect to. There are no side effects from setting this property higher, and the only affect would be an improved message processor proxy request processing times.
Note: Edge for Private Cloud version 50.00 has the default setting of 500. |
| Multiple entries for key value maps | 157933959: Concurrent inserts and updates to the same key value map (KVM) scoped to the organization or environment level causes inconsistent data and lost updates. Note: This limitation only applies to Edge for Private Cloud. Edge for Public Cloud and Hybrid do not have this limitation. For a workaround in Edge for Private Cloud, create the KVM at the
|