您正在查看 Apigee Edge 文档。
转到
Apigee X 文档。 info
以下各部分介绍了 Apigee Edge 和 Edge for Private Cloud 的已知问题。在大多数情况下,列出的问题会在未来的版本中更正。
其他 Edge 已知问题
以下各部分介绍了 Edge 的各种已知问题。
| 区域/摘要 | 已知问题 |
|---|---|
缓存过期导致 cachehit 值不正确 |
在 LookupCache 政策之后使用 解决方法:在第一次通话后立即重复此过程(进行第二次通话)。 |
将 InvalidateCache 政策 PurgeChildEntries 设置为 true 不起作用 |
在 InvalidateCache 政策中设置 解决方法:使用 KeyValueMapOperations 政策迭代缓存版本,从而无需进行缓存失效。 |
| 对 SharedFlow 或 API 代理的并发部署请求可能会导致管理服务器中出现不一致的状态,其中多个修订显示为已部署。 |
例如,当使用不同修订版本实现 CI/CD 部署流水线的并发运行时,可能会发生这种情况。为避免此问题,请避免在当前部署完成之前部署 API 代理或 SharedFlow。 解决方法:避免并发 API 代理或 SharedFlow 部署。 |
| Edge API Analytics 中显示的 API 调用次数可能包含重复数据。 |
Edge API Analytics 有时可能会包含 API 调用的重复数据。在这种情况下,Edge API Analytics 中显示的 API 调用次数高于第三方分析工具中显示的类似值。 解决方法:导出 Google Analytics 数据,然后使用 gateway_flow_id 字段删除数据中的重复项。 |
Edge 界面的已知问题
以下几个部分介绍了 Edge 界面的已知问题。
| 领域 | 已知问题 |
|---|---|
| 在将组织映射到身份区域后,无法通过导航栏访问 Edge SSO 区域管理页面 | 将组织连接到身份区域后,您无法再通过选择“管理”>“SSO”从左侧导航栏访问 Edge SSO 区域管理页面。如需解决此问题,请使用以下网址直接导航至页面:https://apigee.com/sso |
Known issues with the integrated portal
The following sections describe the known issues with the integrated portal.
| Area | Known issues |
|---|---|
| SmartDocs |
|
| SAML identity provider | Single logout (SLO) with the SAML identity provider is not supported for custom domains. To enable a custom domain with a SAML identity provider, leave the Sign-out URL field blank when you configure SAML settings. |
| Portal admin |
|
| Portal features |
|
Known issues with Edge for Private Cloud
The following sections describe the known issues with Edge for Private Cloud.
| Area | Known issues |
|---|---|
| Edge for Private Cloud 4.53.01 |
NGINX Vulnerability Assessment (CVE-2026-42945)
A vulnerability (CVE-2026-42945) was disclosed affecting the Impact on Apigee Edge for Private Cloud: Apigee Edge for Private Cloud is not affected by this vulnerability in its default, shipped configuration. The exploitability of CVE-2026-42945 is dependent on specific NGINX configuration patterns, notably the use of the Action Required:
|
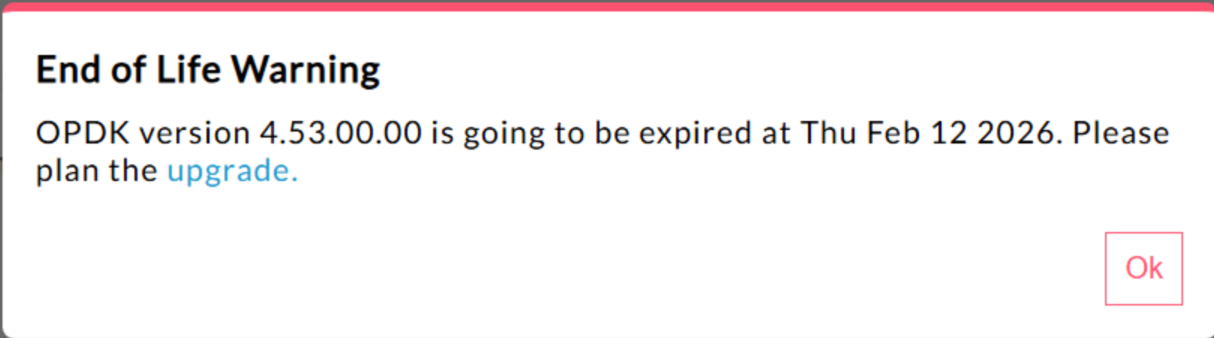
| Edge for Private Cloud 4.53.00 | 440148595: End of Life Popup Warning Displayed Excessively
In Edge for Private Cloud 4.53.00 and later, the UI displays an
"End of Life" (EOL) warning pop-up. This warning
appears There is currently no method available for users to disable or reduce the frequency of this EOL warning. |
| Edge for Private Cloud 4.53.01 |
Java Callouts
Customer Java callouts that attempt to load the Bouncy Castle cryptography provider using the name "BC" might fail because the default provider has been changed to Bouncy Castle FIPS to support FIPS. The new provider name to use is "BCFIPS". |
| Edge for Private Cloud 4.53.00 |
Java Callouts
Customer Java callouts that attempt to load the Bouncy Castle cryptography provider using the name "BC" might fail because the default provider has been changed to Bouncy Castle FIPS to support FIPS. The new provider name to use is "BCFIPS". |
| Edge for Private Cloud 4.52.01 Mint update |
This issue affects only those who are using MINT or have MINT enabled in Edge for Private Cloud installations. Component affected: edge-message-processor Issue: If you have monetization enabled and are installing 4.52.01 as a fresh install or upgrading from previous Private Cloud versions, you will encounter an issue with message processors. There will be a gradual increase in open thread count leading to resource exhaustion. The following exception is seen in edge-message-processor system.log: Error injecting constructor, java.lang.OutOfMemoryError: unable to create new native thread |
| Apigee HTTP/2 vulnerability | A Denial-of-Service (DoS) vulnerability was recently discovered in multiple implementations of the HTTP/2 protocol (CVE-2023-44487), including in Apigee Edge for Private Cloud. The vulnerability could lead to a DoS of Apigee API management functionality. For more details, see Apigee Security Bulletin GCP-2023-032. The Edge for Private Cloud router and management server components are exposed to the internet and can potentially be vulnerable. Although HTTP/2 is enabled on the management port of other Edge-specific components of Edge for Private Cloud, none of those components are exposed to the internet. On non-Edge components, like Cassandra, Zookeeper and others, HTTP/2 is not enabled. We recommend that you take the following steps to address the Edge for Private Cloud vulnerability:
Follow these steps if you are using Edge Private Cloud versions 4.51.00.11 or newer:
Follow these steps if you are using Edge for Private Cloud versions older than 4.51.00.11:
|
| Postgresql upgrade when updating to version 4.52 | Apigee-postgresql is having issues with upgrading from Edge for Private Cloud version 4.50 or 4.51 to version 4.52. The issues mainly occur when the number of tables is greater than 500. You can check the total number of tables in Postgres by running the SQL query below: select count(*) from information_schema.tables Workaround: When Updating Apigee Edge 4.50.00 or 4.51.00 to 4.52.00, be sure to perform the preliminary step before upgrading Apigee-postgresql. |
| LDAP policy | 149245401: LDAP connection pool settings for JNDI configured through the LDAP resource are not reflected, and JNDI defaults cause single-use connections each time. As a result, connections are being opened and closed each time for single use, creating a large number of connections per hour to the LDAP server. Workaround: In order to change the LDAP connection pool properties, do the following steps to set a global change across all LDAP policies.
To verify that your connection pool JNDI properties are taking effect, you can perform a tcpdump to observe the behavior of the LDAP connection pool over time. |
| High Request Processing Latency | 139051927: High proxy processing latencies found in the Message Processor are affecting all API Proxies. Symptoms include 200-300ms delays in processing times over normal API response times and can occur randomly even with low TPS. This can occur when than more than 50 target servers in which a message processor makes connections. Root cause: Message processors keep a cache that maps target server URL to HTTPClient object for outgoing connections to target servers. By default this setting is set to 50 which may be too low for most deployments. When a deployment has multiple org/env combinations in a setup, and have a large number of target servers that exceed 50 altogether, the target server URLs keep getting evicted from cache, causing latencies. Validation: To determine if target server URL eviction is causing the latency problem, search the Message Processor system.logs for keyword "onEvict" or "Eviction". Their presence in the logs indicate that target server URLs are getting evicted from the HTTPClient cache because the cache size is too small. Workaround:
For Edge for Private Cloud versions 19.01 and 19.06, you can edit and configure the HTTPClient
cache, conf/http.properties+HTTPClient.dynamic.cache.elements.size=500 Then restart the message processor. Make the same changes for all message processors. The value 500 is an example. The optimal value for your setup should be greater than the number of target servers that the message processor would connect to. There are no side effects from setting this property higher, and the only affect would be an improved message processor proxy request processing times.
Note: Edge for Private Cloud version 50.00 has the default setting of 500. |
| Multiple entries for key value maps | 157933959: Concurrent inserts and updates to the same key value map (KVM) scoped to the organization or environment level causes inconsistent data and lost updates. Note: This limitation only applies to Edge for Private Cloud. Edge for Public Cloud and Hybrid do not have this limitation. For a workaround in Edge for Private Cloud, create the KVM at the
|