Vous consultez la documentation Apigee Edge.
Accédez à la
documentation Apigee X. info
Les sections suivantes décrivent les problèmes connus liés à Apigee Edge et Edge pour le cloud privé. Dans la plupart des cas, les problèmes répertoriés seront résolus dans une prochaine version.
Divers problèmes connus avec Edge
Les sections suivantes décrivent divers problèmes connus liés à Edge.
| Zone/Récapitulatif | Problèmes connus |
|---|---|
L'expiration du cache entraîne une valeur cachehit incorrecte |
Lorsque la variable de flux Solution:répétez la procédure (passez un deuxième appel) juste après le premier appel. |
Définir la règle InvalidateCache PurgeChildEntries sur "true" ne fonctionne pas correctement |
Définir Solution de contournement:utilisez la règle KeyValueMapOperations pour itérer la gestion des versions du cache et éviter d'avoir à invalider le cache. |
| Les requêtes de déploiement simultanés pour un flux SharedFlow ou un proxy d'API peuvent entraîner un état incohérent sur le serveur de gestion, où plusieurs révisions sont affichées comme étant déployées. |
Cela peut se produire, par exemple, en cas d'exécutions simultanées d'un pipeline de déploiement CI/CD qui exploitent des révisions différentes. Pour éviter ce problème, évitez de déployer des proxys d'API ou des flux SharedFlow avant la fin du déploiement actuel. Solution:Évitez les déploiements simultanés de proxys d'API ou de flux SharedFlow. |
| Les nombres d'appels d'API affichés dans Edge API Analytics peuvent contenir des données en double. |
L'API Analytics Edge peut parfois contenir des données en double pour les appels d'API. Dans ce cas, les totaux affichés pour les appels d'API dans Edge API Analytics sont supérieurs aux valeurs comparables affichées dans les outils d'analyse tiers. Solution:Exportez les données d'analyse et utilisez le champ gateway_flow_id pour dédupliquer les données. |
Known issues with the Edge UI
The following sections describe the known issues with the Edge UI.
| Area/Summary | Known issues |
|---|---|
| Can't access Edge SSO Zone Administration page from navigation bar after organization is mapped to an identity zone |
When you connect an organization to an identity zone, you can no longer access the Edge SSO Zone Administration page from the left navigation bar by selecting Admin > SSO. Workaround: Navigate to the page directly using the following URL: https://apigee.com/sso |
| Edge UI TLS Configuration |
The options Workaround: Follow the steps below to enable specific ciphers for the Edge UI:
|
Problèmes connus liés au portail intégré
Les sections suivantes décrivent les problèmes connus liés au portail intégré.
| Zone | Problèmes connus |
|---|---|
| SmartDocs |
|
| Fournisseur d'identité SAML | La déconnexion unique (SLO) avec le fournisseur d'identité SAML n'est pas disponible pour les domaines personnalisés. Pour activer un domaine personnalisé avec un fournisseur d'identité SAML, laissez le champ Sign-out URL (URL de déconnexion) vide lorsque vous configurez les paramètres SAML. |
| Administrateur de portail |
|
| Fonctionnalités du portail |
|
Known issues with Edge for Private Cloud
The following sections describe the known issues with Edge for Private Cloud.
| Area | Known issues |
|---|---|
| Edge for Private Cloud 4.53.01 |
NGINX Vulnerability Assessment (CVE-2026-42945)
A vulnerability (CVE-2026-42945) was disclosed affecting the Impact on Apigee Edge for Private Cloud: Apigee Edge for Private Cloud is not affected by this vulnerability in its default, shipped configuration. The exploitability of CVE-2026-42945 is dependent on specific NGINX configuration patterns, notably the use of the Action Required:
|
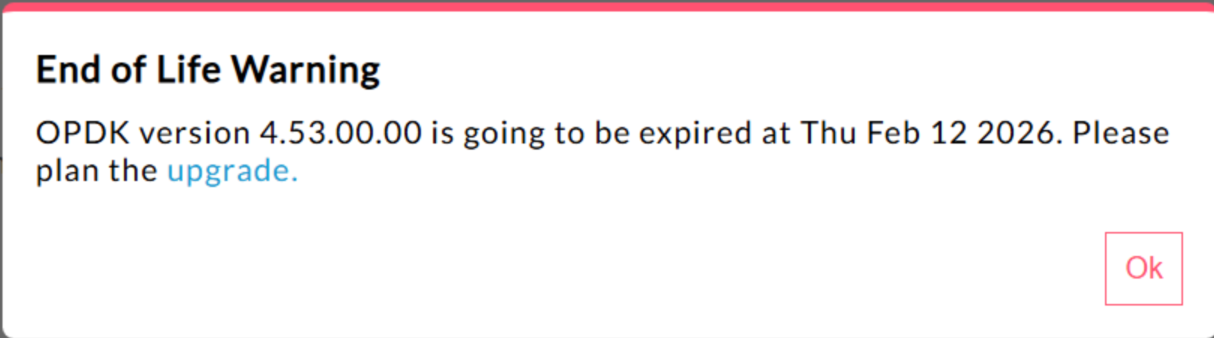
| Edge for Private Cloud 4.53.00 | 440148595: End of Life Popup Warning Displayed Excessively
In Edge for Private Cloud 4.53.00 and later, the UI displays an
"End of Life" (EOL) warning pop-up. This warning
appears There is currently no method available for users to disable or reduce the frequency of this EOL warning. |
| Edge for Private Cloud 4.53.01 |
Java Callouts
Customer Java callouts that attempt to load the Bouncy Castle cryptography provider using the name "BC" might fail because the default provider has been changed to Bouncy Castle FIPS to support FIPS. The new provider name to use is "BCFIPS". |
| Edge for Private Cloud 4.53.00 |
Java Callouts
Customer Java callouts that attempt to load the Bouncy Castle cryptography provider using the name "BC" might fail because the default provider has been changed to Bouncy Castle FIPS to support FIPS. The new provider name to use is "BCFIPS". |
| Edge for Private Cloud 4.52.01 Mint update |
This issue affects only those who are using MINT or have MINT enabled in Edge for Private Cloud installations. Component affected: edge-message-processor Issue: If you have monetization enabled and are installing 4.52.01 as a fresh install or upgrading from previous Private Cloud versions, you will encounter an issue with message processors. There will be a gradual increase in open thread count leading to resource exhaustion. The following exception is seen in edge-message-processor system.log: Error injecting constructor, java.lang.OutOfMemoryError: unable to create new native thread |
| Apigee HTTP/2 vulnerability | A Denial-of-Service (DoS) vulnerability was recently discovered in multiple implementations of the HTTP/2 protocol (CVE-2023-44487), including in Apigee Edge for Private Cloud. The vulnerability could lead to a DoS of Apigee API management functionality. For more details, see Apigee Security Bulletin GCP-2023-032. The Edge for Private Cloud router and management server components are exposed to the internet and can potentially be vulnerable. Although HTTP/2 is enabled on the management port of other Edge-specific components of Edge for Private Cloud, none of those components are exposed to the internet. On non-Edge components, like Cassandra, Zookeeper and others, HTTP/2 is not enabled. We recommend that you take the following steps to address the Edge for Private Cloud vulnerability:
Follow these steps if you are using Edge Private Cloud versions 4.51.00.11 or newer:
Follow these steps if you are using Edge for Private Cloud versions older than 4.51.00.11:
|
| Postgresql upgrade when updating to version 4.52 | Apigee-postgresql is having issues with upgrading from Edge for Private Cloud version 4.50 or 4.51 to version 4.52. The issues mainly occur when the number of tables is greater than 500. You can check the total number of tables in Postgres by running the SQL query below: select count(*) from information_schema.tables Workaround: When Updating Apigee Edge 4.50.00 or 4.51.00 to 4.52.00, be sure to perform the preliminary step before upgrading Apigee-postgresql. |
| LDAP policy | 149245401: LDAP connection pool settings for JNDI configured through the LDAP resource are not reflected, and JNDI defaults cause single-use connections each time. As a result, connections are being opened and closed each time for single use, creating a large number of connections per hour to the LDAP server. Workaround: In order to change the LDAP connection pool properties, do the following steps to set a global change across all LDAP policies.
To verify that your connection pool JNDI properties are taking effect, you can perform a tcpdump to observe the behavior of the LDAP connection pool over time. |
| High Request Processing Latency | 139051927: High proxy processing latencies found in the Message Processor are affecting all API Proxies. Symptoms include 200-300ms delays in processing times over normal API response times and can occur randomly even with low TPS. This can occur when than more than 50 target servers in which a message processor makes connections. Root cause: Message processors keep a cache that maps target server URL to HTTPClient object for outgoing connections to target servers. By default this setting is set to 50 which may be too low for most deployments. When a deployment has multiple org/env combinations in a setup, and have a large number of target servers that exceed 50 altogether, the target server URLs keep getting evicted from cache, causing latencies. Validation: To determine if target server URL eviction is causing the latency problem, search the Message Processor system.logs for keyword "onEvict" or "Eviction". Their presence in the logs indicate that target server URLs are getting evicted from the HTTPClient cache because the cache size is too small. Workaround:
For Edge for Private Cloud versions 19.01 and 19.06, you can edit and configure the HTTPClient
cache, conf/http.properties+HTTPClient.dynamic.cache.elements.size=500 Then restart the message processor. Make the same changes for all message processors. The value 500 is an example. The optimal value for your setup should be greater than the number of target servers that the message processor would connect to. There are no side effects from setting this property higher, and the only affect would be an improved message processor proxy request processing times.
Note: Edge for Private Cloud version 50.00 has the default setting of 500. |
| Multiple entries for key value maps | 157933959: Concurrent inserts and updates to the same key value map (KVM) scoped to the organization or environment level causes inconsistent data and lost updates. Note: This limitation only applies to Edge for Private Cloud. Edge for Public Cloud and Hybrid do not have this limitation. For a workaround in Edge for Private Cloud, create the KVM at the
|